
Blog · page 6
Notes on engineering, design, and everything in between.
What a CVSS 4.0 score of 9.2 says, and the three things it does not
Both PHP vulnerabilities today are rated CVSS v4.0 9.2. That number is a filter, not a priority: it measures the vulnerability, not your assets, your exposure, or the cost of patching.
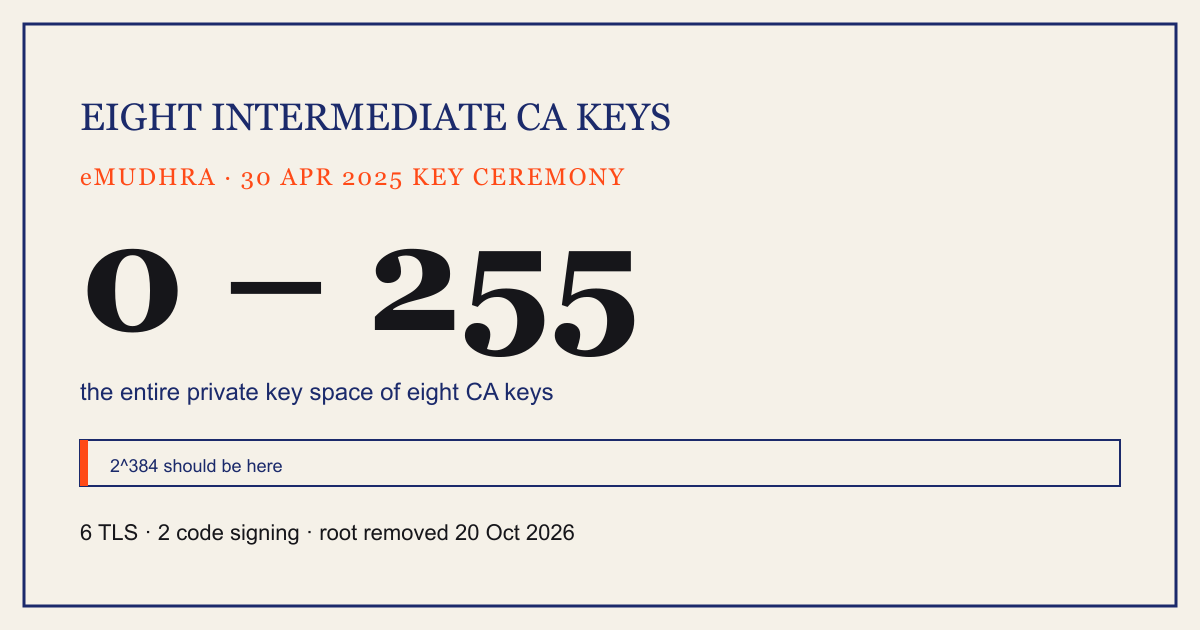
Eight intermediate CA private keys that were all integers below 256
Someone scanned the CCADB certificate corpus and found that eight eMudhra intermediate CA keys could simply be enumerated — they were generated as integers between 0 and 255. Yesterday Mozilla decided to remove trust in emSign ECC Root CA - G3.
PHP ships two 9.2 fixes today at 14:00 UTC: what to do before then
PHP posted an advance notice on 20 October: a security release on 21 October at 14:00 UTC fixes two vulnerabilities, both rated CVSS v4.0 9.2. Details come with the release, but your rollback plan can be settled now.
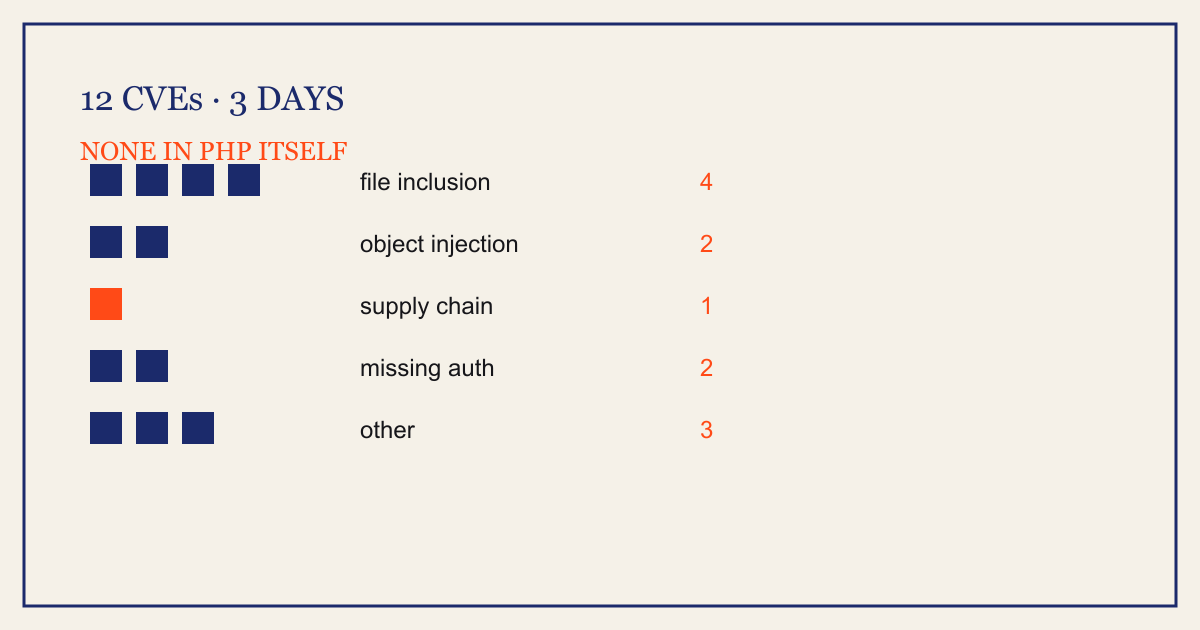
Twelve PHP CVEs in three days, none of them in PHP
I pulled every PHP-related advisory NVD published between 19 and 21 October. All twelve are plugins, CMS modules and libraries. That is the more useful signal: your real inventory is not the language.
Ten open-source games, 48 MB: what self-hosting third-party games actually costs
I vendored ten MIT/public-domain HTML5 games into this static site — 48.4 MB in total. The work was not copying files; it was licences, size, and the fact that all of them loaded things from CDNs.
When a 3D scene should actually start loading
Fourteen Three.js scenes on one site is not a rendering problem, it is a scheduling problem. Two gates, one SPA navigation bug, and the WebGL context I forgot to release.