
Blog · page 7
Notes on engineering, design, and everything in between.
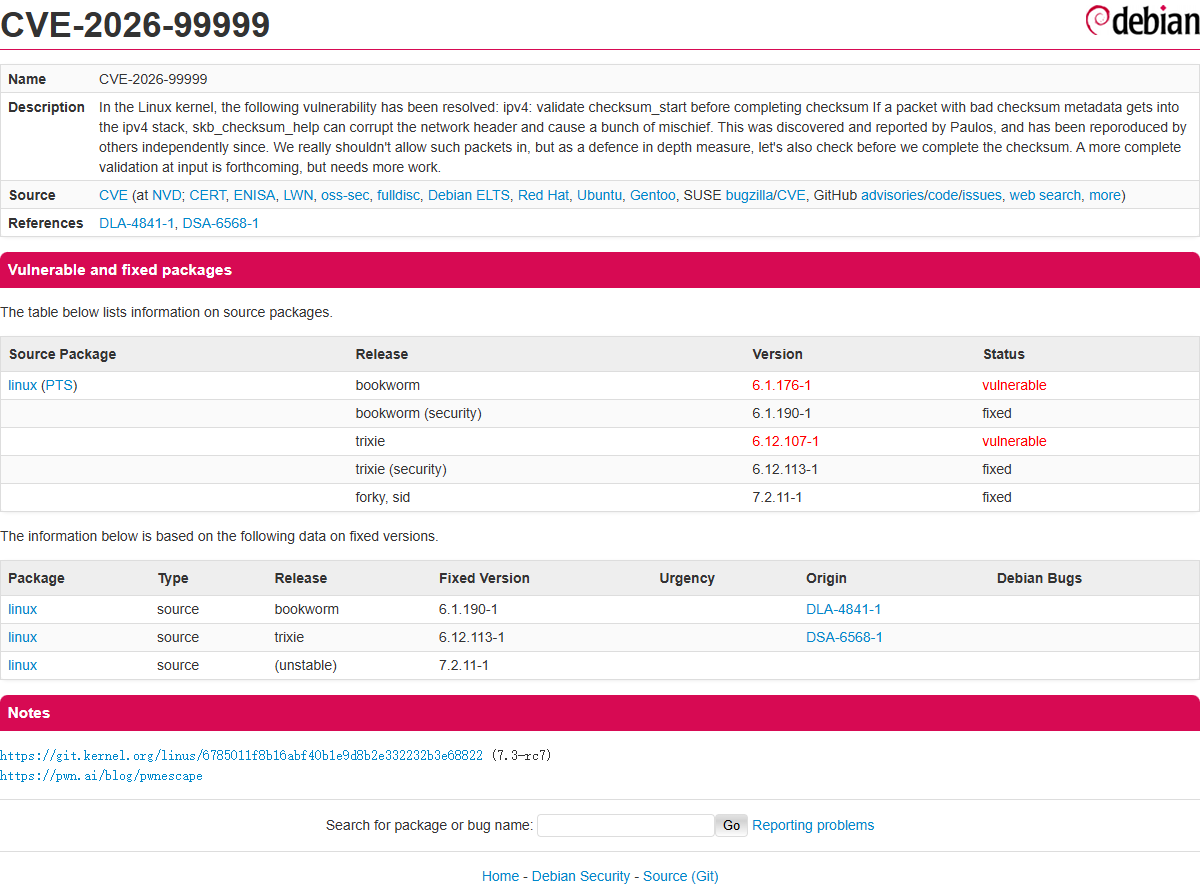
CVE-2026-99999: the IPv4 checksum bug that can escape a VM
Debian security tracker lists CVE-2026-99999 as a missing IPv4 checksum check in the Linux kernel, exploitable from a guest to the KVM host. Fixed in 6.1.190-1 (bookworm) and 6.12.113-1 (trixie).
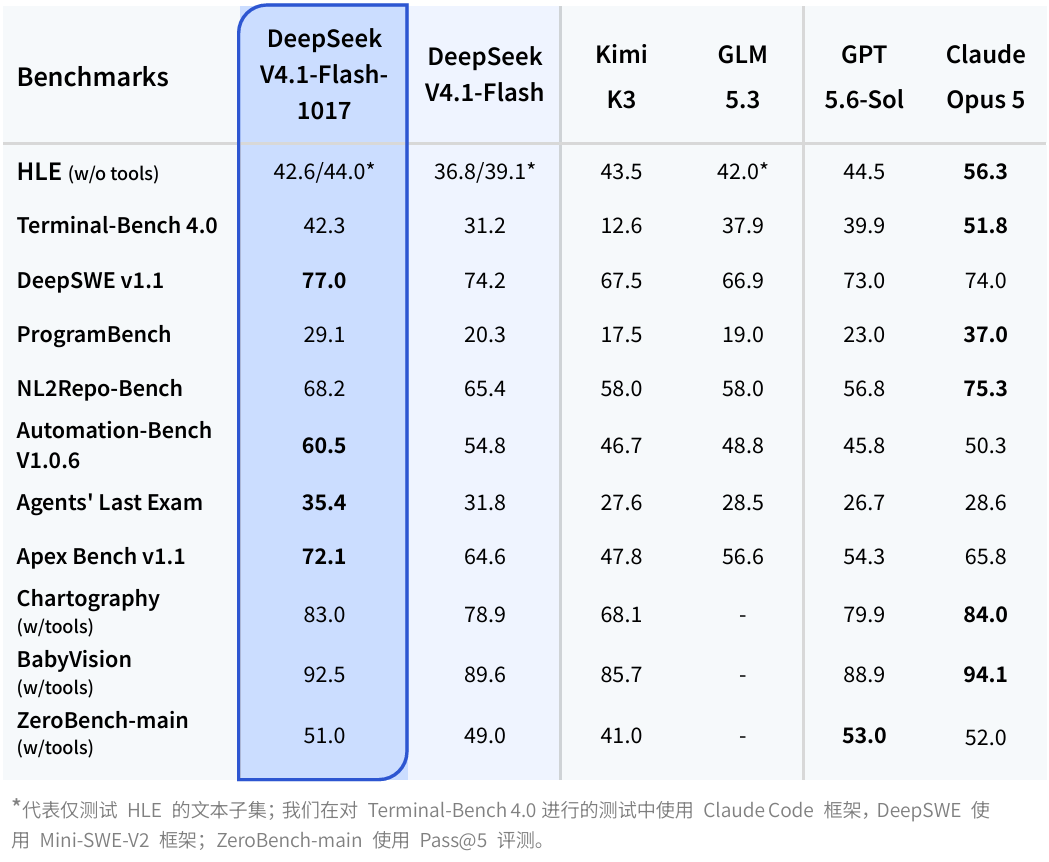
Reading DeepSeek official charts: what V4.1 Flash-1017 actually improves
I pulled the benchmark table, the performance-cost chart and the case images from DeepSeek's official changelog. The update is about doing work, not about being smarter — and the price did not change.
Klotski: write the rules before the animation
Sliding puzzles are not hard because of the board, but because of "can this piece move". Flatten 4x5 into occupancy, get the check in three lines, and use BFS instead of A*.
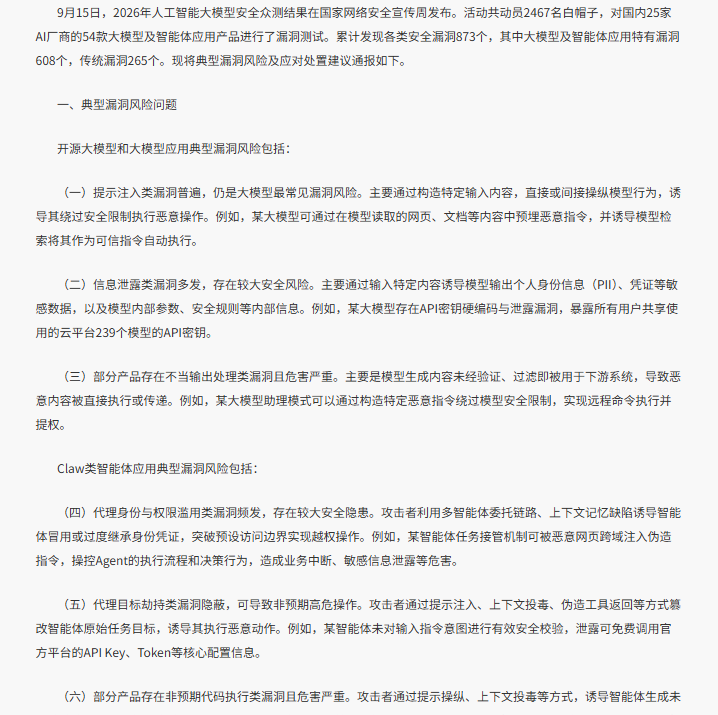
873 bugs, 54 models: notes on the 2026 LLM security report
2,467 white hats tested 54 LLM and agent products from 25 vendors and found 873 vulnerabilities, 608 of them LLM-specific. Prompt injection still ranks first; a hardcoded API key exposed keys for 239 models at once.
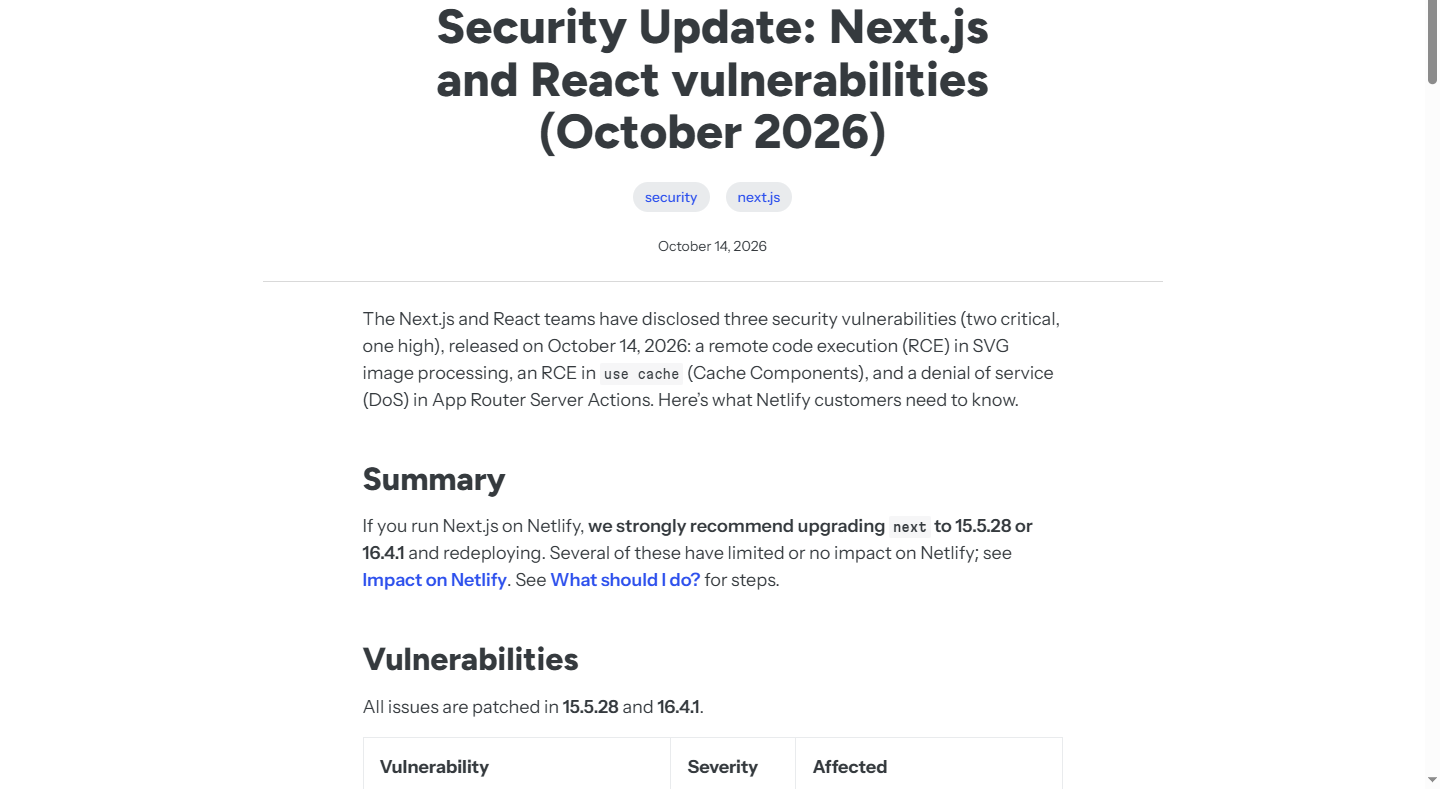
Next.js October patch: three holes, two of them remote code execution
In mid-October Next.js and React shipped three vulnerabilities: an image-processing RCE, a use cache RCE and a Server Action denial of service. The patches are out of band — do not wait for the next minor version.
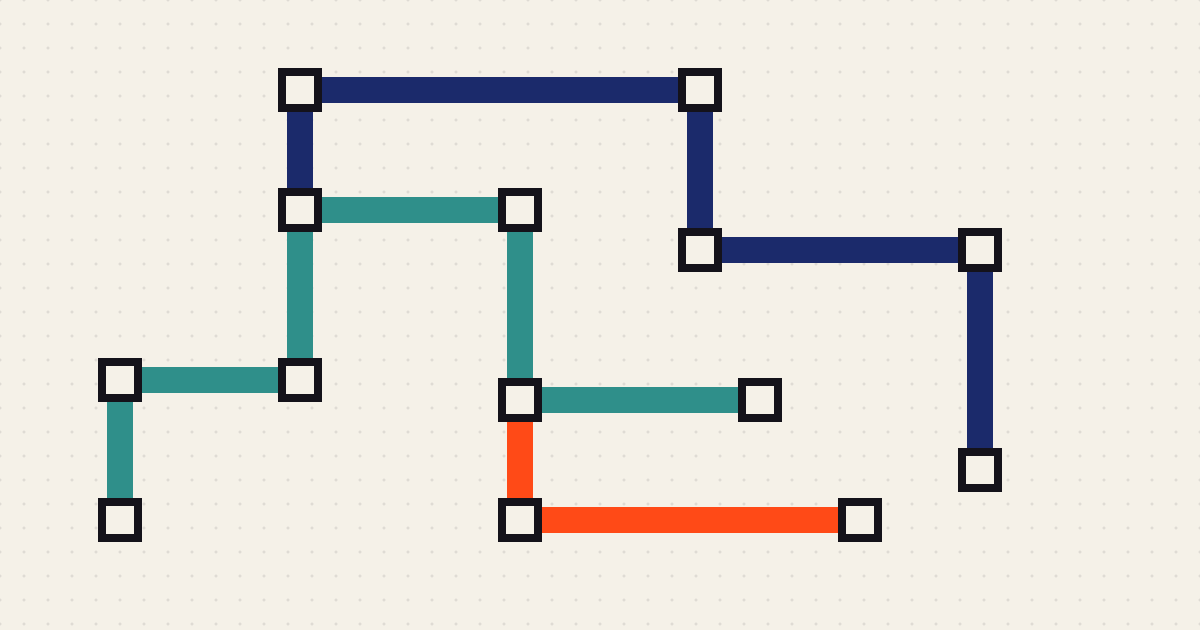
Pipe puzzles: guarantee the map is solvable
Random pipe orientations mostly produce unsolvable boards. Generate a spanning tree first, then rotate every cell — solvability comes from the construction, not from a check.